 LuckyCharmGold Account Safety Features
We at LuckyCharmGold have developed secure methods for providing OSRS accounts to our customers. No other OSRS account providers are operating the way we do. On this page, we will tell you everything we do to keep our OSRS accounts safe with training & how we provide the best experience possible that gives you great confidence as a customer when buying OSRS accounts from us.
🚀Original Jagex Launcher account creation🚀
Every account is created by us on the official OSRS website, so it can never be recovered.
We create original Jagex Launcher accounts on the official OSRS website. These are the safest accounts to buy because they have no recovery process and are therefore non-recoverable. This means that once the email address of the account is changed, the account is 100% yours and can not be recovered. Not even by us. Check the official Jagex Website to see what they say if you lost access to your Jagex Launcher email, and confirm it yourself.

Jagex's own support page on lost access to a Jagex Account email.
 Created & 100% hand-trained in the United States
Created and trained from the US, where most of the player base is.
We chose to do this because the majority of the player base is from the United States, and therefore it is also best to choose this country to create accounts from & train accounts in without raising suspicion. It would also mean that for people buying the account from us in the United States, there wouldn’t be any country changes when taking ownership.
Not from the United States? Don’t worry. We always rest our accounts for at least a few days before transferring ownership to you. People move countries all the time when they are on holiday or when they are moving. We have never received an account ban before by transferring ownership this way.
 Features of our Account Safety Plugin
A custom RuneLite plugin that controls how every account is trained.
Our customized RuneLite plugin is something we took a long time developing & perfecting. This plugin makes sure that accounts are trained in the safest way possible.
🔐Giving Workers Account Access🔐
We give workers account access through our custom-made RuneLite plugin. This allows us to give workers access to Jagex Launcher accounts without them knowing the login credentials. When they enter an account, they will see this upon login.

What a worker sees when logging in through the plugin.
 Enforcing VPN Usage
Our plugin will only let workers connect to the account when they have a VPN active from the United States. This ensures that there is no IP leakage from countries where our workers are from. It also has a built-in kill switch, dropping the connection in case of a disconnect, which ensures no IP leakage. On top of that, we also ask our workers to use kill-switch features on their VPN.
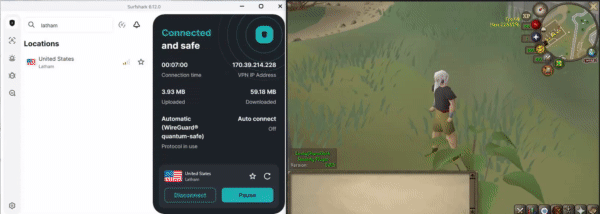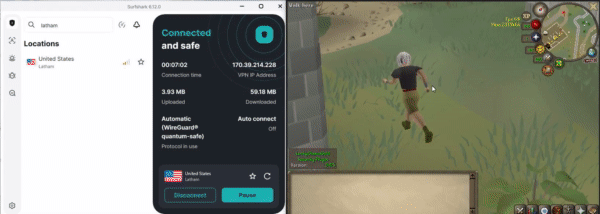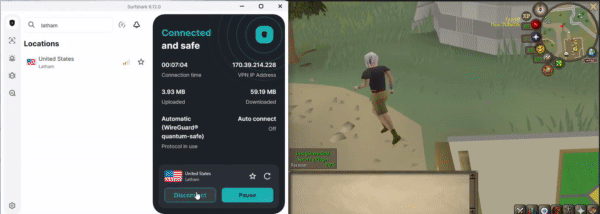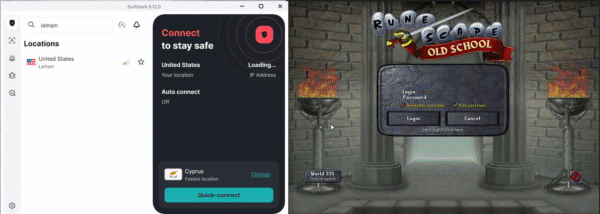
The plugin shuts down RuneLite immediately, before the connection can re-establish and leak my own IP address.
❌Disabled External Plugins❌
Our account safety plugin doesn’t work with any other external plugins in the RuneLite folder. If any 3rd party plugins are being put in the “external-plugin” folder or “side-loaded plugin” folder, workers will not be able to use our plugin, and therefore not be able to connect to any account. This ensures that workers don’t use any illegal third-party plugins to train accounts, and we are sure that all training is 100% done manually.
📸Tracking Account Activity📸
We track daily account activity with screenshots to make sure that workers are not using illegal macroing software to train accounts. We also make sure that workers do not train for long hours doing the same activity for days on end, because, before this, it sometimes caused fake “macroing bans”. Basically, since our workers are playing these accounts on a VPN, doing repetitive tasks, this caused Jagex to believe they were macroing, but these were “false positive bans”. Therefore, we ensure we change training activities and locations to address this problem. Unfortunately, their macroing system is in no way “accurate”. Most of their macroing bans are looking at behaviour, and if you behave like a bot, you can expect to be falsely banned.

A daily activity screenshot from the plugin.
Original Owner & In-House Team
We created every account we sell, and our own team trained it.
We are the original owners of all the accounts we sell. That way, we can ensure you that there will never be any recoveries down the line. We never rebuy accounts from other customers or sell customers’ accounts. This gives our customers the greatest confidence in buying from us, and gives you complete peace of mind.
We also have our in-house team of workers who train these accounts. We never use bulk account suppliers to resell accounts, which allows us to offer the lowest prices possible because we pay our account trainers directly, without any middlemen involved.